ISO 31030:2021 Consulting • Assessment • Audit Readiness

ISO 31030 Travel Risk
Management

ISO 31030:2021 Consulting & Assessment

Sicuro makes ISO 31030 travel risk management practical. We integrate policy, roles, and controls into a single framework and coordinate your insurer, communications, tracking platform, and local operators under one operator-led playbook. We ensure compliance is embedded in your daily operations: evidence is audit-ready, responsibilities are clear, and every incident or routine task is managed through one point of contact, without duplication of services.
Trusted by Hundreds of Leading Organizations Worldwide
Bloomberg logo - Sicuro Group
UK foreign commonwealth development office
US Department of State
embassy-of-the-kingdom-of-the-netherlands-logo-min

Benefits of ISO 31030 Travel Risk Management

ISO 31030 is about readiness, not paperwork. If you’re benchmarking travel risk management program against iso 31030 standards, these are the three outcomes that matter—each one backed by evidence your auditors, insurers and board can trust.

Protect people. Prove it.

ISO 31030 exists to keep travellers healthy, safe and secure. We build the controls to do exactly that—clear roles and approvals, risk assessment, tailored briefings, two‑way communications, traveller tracking and GSOC response—so people avoid harm, get help faster and return home safely. The documentation and decision logs come with the territory; they demonstrate diligence to boards, insurers and regulators, but the primary outcome is human safety.

Fewer disruptions, stronger continuity

Pre-trip approvals, live intelligence, GSOC monitoring, two-way alerts and traveller tracking cut time-to-locate, accelerate assistance and keep trips on-mission. The result is tighter business continuity and resilience across destinations, including higher-risk markets, without slowing the business.

Stakeholder assurance, market access

ISO 31030 alignment gives boards, investors and insurers confidence that controls are effective and proportionate. Sicuro integrates with your TMC and HRIS so the programme scales cleanly, supports entry into tougher markets, and can even contribute to premium reductions when governance is demonstrably robust.

ISO 31030:2021 Compliance - Made Practical

ISO 31030 isn’t paperwork; it’s proof of readiness. Sicuro Group builds and operates the exact controls the standard expects—and we can evidence each one on demand. If you’re benchmarking trm program against iso 31030 standards, the elements below map directly to the clauses auditors look for.

Governance & Policy

Board‑level ownership, a signed TRM policy, roles and accountability. We embed decision rights, approval thresholds, and an exception process so travel risk is managed like any other enterprise risk.

Risk Assessment & Intelligence

Destination ratings, traveller profile checks, and itinerary‑specific assessments backed by live intelligence. We standardise likelihood/consequence scoring so approvals are defensible.

Pre‑Trip Authorisation & Briefings

Single approval workflow with medical/visa checks, documented mitigations and mandatory briefings. Residual risk is signed off, not assumed.

Communications & Mass Notification

Two‑way comms, duress protocols and multi‑channel alerts (SMS, WhatsApp, email, voice, app). We script escalation paths and test them quarterly.

GSOC & Incident Management

24/7 multilingual GSOC monitors events, runs checks‑in, and activates incident/crisis teams. Playbooks cover medical, security and logistical disruptions.

Traveller Tracking

GPS/satellite tracking with privacy controls, geofences and proof‑of‑life check‑ins. Location data is used for duty‑of‑care—not surveillance.

Secure Transport & Journey Management

Vetted drivers, meet‑and‑greet, route selection and movement windows. Executive protection and safe accommodation when risk dictates.

Medical/Security Support & Insurance‑First

24/7 medical and security advisory, local care access, and insurer‑authorised pathways for direct billing. No duplicate assistance contracts—just faster care and cleaner claims.

Evacuation Planning

Pre‑arranged med/non‑med/security evacuation options with mobilization SLAs. We rehearse, document triggers and record decision logs.

Monitoring, Metrics & Benchmarking

Quarterly KPIs, traveller surveys and internal reviews to drive continuous improvement. We support external benchmarking trm program against iso 31030 standards to evidence maturity.

Recording, Reporting & Data Protection

Version‑controlled records for policies, risk assessments, briefings, incidents and escalations, held under strict privacy controls. If it isn’t written, it didn’t happen.

Seamless Implementation

Direct TMC and HRIS/API feeds ingest itineraries and profiles to automate risk triage, approvals and alerts—minimising disruption while raising assurance.

Outcome: a single, auditable system that meets ISO 31030 expectations and proves duty of care—without slowing travel down.

Travel Risk Management

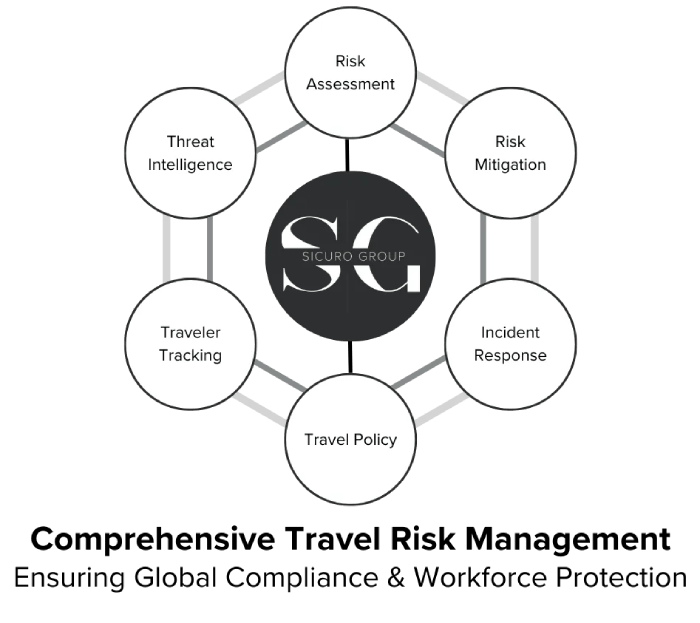
Sicuro Group’s travel risk management program aligns with ISO 31030:2021, the international standard for travel risk management, ensuring your organization meets global best practices for managing travel-related risks. Our ISO 31030-aligned approach provides a structured framework for identifying, assessing, and mitigating travel risks—helping you fulfill your duty of care obligations while streamlining governance and compliance.

Countries Covered
0 +
Global Assistance
0 /7
Response Time
0 s
Client Retention
0 %

ISO 31030:2021-compliant - 24/7 GSOC – Uninsured events handled

Pre-Travel
Alertmedia Pre Travel Screen
During Travel
Alert Media and Sicuro Group dashboard for travel threat intelligence, workforce and asset tracking, mass communication and traveller tracking along with the mobile view of communication for travellers through email, SMS, Voice, text and WhatsApp
In Emergency
Alert Media and Sicuro Group dashboard and alerts for crisis management

Who calls whom — simple flow

1. Medical emergency:
Traveler or manager calls Sicuro hotline → we engage the insurer’s assistance team for authorization & direct billing → Sicuro coordinates all local logistics.
2. Security or evacuation: 
Traveler or manager calls Sicuro hotline → our operators coordinate security, political, or evacuation response directly → no insurer routing required.
3. Coverage change mid-trip: 
Traveler or manager calls Sicuro hotline → seamless switch to uninsured response → no dead ends.

ISO 31030 controls satisfied

What Our Clients Say

Trusted by leading organizations worldwide

Head of Operations, Business Protection

Global Media Company, New York, USA

We are getting great compliments from the travelers about the support they are getting from you and the team on the ground in Kinshasa. Apparently, Kinshasa is the most “chaotic” place they have visited, so they really appreciate the support and they feel a lot at ease with your support. Wanted to pass on the compliments and to say that we are very happy to be working with you in this area of travel security.

Travel Security Manager

Technology Company

Sicuro Group’s exceptional service during a critical evacuation was nothing short of remarkable. Their professionalism, efficiency, and ability to navigate complex situations were impressive. I highly recommend Sicuro Group to any company seeking reliable support for evacuation services in Middle East. They truly deliver when it matters most.

Managing Director

UK Prime Contractor

Sicuro continues to provide a high level of operational support in high-risk areas to meet the demands of our business needs. Extremely responsive, Ivana and her team maintain strong lines of communication throughout the entirety of the tasks and execute contingency plans seamlessly.
GSOC Manager

International News Agency, Paris France

Appreciate the constant movement updates during the operations. And thank you for ensuring the safety and security of our travelers throughout.

What Are the Most Common Risks for Business Travelers?

Most programmes look fine on paper. The real test is readiness. Use this as a quick reality‑check across the eight risk areas we see most often in corporate travel.

Health & Medical

From infectious disease and poor local care to environmental exposure and chronic conditions, health risk is the most predictable—and the most neglected—risk to manage pre‑trip.

Security & Crime

Theft, assault, targeted crime and terrorism remain credible in some markets. Vet routes and accommodation, brief travellers, and define do‑not‑travel triggers up front.

Political & Civil Unrest

Protests, curfews, border closures and sudden policy shifts can strand travellers or shut down routes. Build in fast approval paths for diversion or denial of travel.

Natural Hazards & Extreme Weather

Earthquakes, storms and floods disrupt flights, power and comms. Pre‑plan alternates and extraction routes; treat cascading disruption as the norm, not the edge case.

Cultural & Legal Exposure

Missteps on local laws, speech or customs can escalate to fines, detention or loss of access. Pre‑trip briefings and clear conduct guidelines reduce avoidable incidents.

Road & Transport Safety

Road traffic incidents remain a leading cause of harm. Focus on journey planning, vetted drivers, vehicle standards and fatigue management over paper policies.

Mental Wellbeing & Fatigue

Jet lag, isolation and sustained pressure degrade judgement and reaction times. Build in rest, access to support, and permission to abort when judgement is impaired.

Data & Privacy (Cyber)

Supporting deployments and humanitarian missions in hostile environments

If you can’t evidence controls across these areas—before, during and after travel—you have exposure. Run the checklist, fix what fails, and keep it lean.

Which Sectors are Benefiting From ISO 31030 Consulting?

Leading Fortune 500 companies rely on Sicuro Group ISO 31030 compliance to protect their most valuable assets, their people.

Technology

Supporting executives from global tech firms during international travel

Finance

Protecting financial services and investment personnel in emerging markets

FMCG

Ensuring safety for consumer goods executives in distribution territories

Management Consulting

Facilitating secure client visits
in high-risk regions

Energy & Resources

Protecting personnel at remote sites and during site visits

Security

Partnering with global security firms requireing regional expertise

Pharmaceutical

Safeguarding R&D teams during international travel

NGOs

Supporting humanitarian missions in challenging environments

Worldwide Coverage

Our network of vetted security partners extends across the globe, with particular expertise in:

Middle East
Africa
Latin America
Asia-Pacific
Europe

Our Risk Management Leaders

Our leadership team brings decades of combined experience in international security, executive protection, and complex logistics management across the world's most challenging regions.

Rafal Hyps
Rafal Hyps

CEO

River Jangda
River Jangda

Commercial Operations Director

Charis Thornton
Charis Thornton

Executive Manager

ISO 31030 Travel Risk Management Audit Checklist

ISO 31030 Travel Risk Management Audit Checklist

This comprehensive checklist is designed to help organizations audit their travel risk management program against ISO 31030:2021 (Travel Risk Management – Guidance for Organizations).

Frequently Asked Questions

ISO 31030:2021 is the international guidance on how organizations should manage travel-related risks to both the organization and its travelers. It sets out a structured approach for building and running a TRM program—covering policy, program development, threat and hazard identification, risk assessment, and prevention/mitigation strategies—and it applies to organizations of any size or sector. It draws on the ISO 31000 risk-management framework and defines core TRM terms and processes (e.g., “travel risk management,” “risk assessment,” “risk treatment”).  

The standard’s aim is cultural as well as operational: to ensure travel risks are taken seriously, resourced properly, and managed effectively—so organizations protect people and assets, reduce legal/financial exposure, enable business in higher-risk locations, and strengthen continuity and resilience. It also highlights the need to map stakeholders and traveler profiles and to record/report lessons learned—practical elements that make a program auditable.  

We operationalize the guidance so you can demonstrate conformance: a single emergency number with clear roles and decision rights; structured, trip-by-trip risk assessment; a travel policy aligned to your standards; platform-enabled communications and traveler tracking with privacy controls; and documented, operator-led incident response.  
 
ISO 31030 evidence by design: roles, journey risk assessments, traveler communications, timelines and outcomes are recorded as we work—audit-ready. The program is reviewed regularly with lessons learned across plan, assess and treat, operate, record and report, and improve. 

ISO 31030 provides a structured framework that helps organizations:

– Demonstrate duty of care with auditable policies and records.

– Clarify roles and responsibilities for better governance.

– Assess and mitigate risks for each trip consistently.

– Strengthen incident response, communication, and traveler tracking.

– Monitor performance and improve processes over time.

– Avoid duplication of services, reducing costs.

– Align with best practices, reducing legal and reputational risks.

– Scale travel risk management to any size of organization.

With Sicuro Group, companies can implement ISO 31030 by:

– Setting clear policies, roles, and governance for travel risk management.

– Conducting trip-by-trip risk assessments before approving travel.

– Using tools for traveler communication, tracking, and real-time alerts.

– Establishing strong incident response and crisis protocols.

– Keeping audit-ready records, KPIs, and regularly reviewing performance.

– Providing training and awareness for both staff and travelers.

– Starting with core modules and scaling up while integrating with existing systems.

Start by mapping what you already do to the structure ISO 31030 expects—policy and governance, programme design, threat and hazard identification, risk assessment, and prevention/mitigation—then use our eight-step audit to test each control in the real world. If you can’t evidence a step, you’ve got exposure; fix the failure before you write new paperwork. ISO 31030 is explicit about a structured cycle of development, implementation, evaluation and review—so keep the process lean but auditable, with decisions and outcomes recorded. Run the checklist quietly, close the gaps, and you’ll have a defensible, standards-aligned programme that works when it matters.

They expect an approved and communicated policy, pre-travel risk assessments tied to destination and activity, evidence of briefings and training, traveller contactability and tracking, tested incident communications, and management reviews with corrective actions. Track completion of briefings and training, time to locate and contact travellers, time to activate assistance, and the proportion of trips denied or altered due to risk; if you handle sensitive information on the road, fold device/cyber control performance into the same dashboard. That’s the practical expression of ISO 31030’s “implement → evaluate → review” loop, supported by Annex A’s emphasis on recording, reporting and provider performance, plus mainstream guidance on maintaining two-way communication in emergencies.

Yes. The standard was written for all kinds of organizations and expects you to right-size controls to your exposure and capacity. In practice, that means a small NGO working in one higher-risk region may weight the programme toward stronger pre-travel approvals, local partners and on-the-ground support, while a mid-market firm with lower-risk, frequent travel focuses on rapid briefings, automated alerts and simple locator protocols. The test is whether your controls are consistent, explainable and reviewable against your risk appetite; ISO 31030 explicitly calls for treatments tailored to the destination and individual.

Treat them as extensions of your control environment, not substitutes. Contract for data flows, SLAs and reports that prove traveler tracking and two-way incident communications are operational; assign clear decision rights for diversion or evacuation and test the hand-offs. ISO 31030 anticipates this: communicate policy and exceptions to the TMC, monitor provider performance as part of programme evaluation, and keep authority lines unambiguous so speed is never in doubt.

No. ISO 31030:2021 is a voluntary guidance standard. It sets out a structured, best-practice framework for travel risk management—but adoption is discretionary unless a regulator, client, contract, or internal policy makes it a requirement. In practice, many organizations use ISO 31030 to demonstrate duty of care and create audit-ready evidence (clear roles, risk assessments, communications, and incident records

With Sicuro’s ISO 31030 consulting, organizations can expect a practical, operator-led approach to travel risk management that aligns policy, governance, risk assessments, traveler tracking, communications, and incident response into one auditable framework. Services include TRM program assessment and benchmarking, gap analysis, policy and governance development, ISO 31030-aligned implementation support, traveler risk assessments, GSOC integration, crisis response planning, KPI monitoring, and audit-ready documentation. Sicuro also helps integrate existing insurers, TMCs, HRIS platforms, and communication tools into a single coordinated travel risk management program designed to improve duty of care, business continuity, and operational resilience.

Insights & Resources

Close-up of the SicuroPeople mobile app with a user pressing the SOS emergency button for instant safety alerts and emergency assistance.
Best Travel Safety Apps for Secure Business Travel in 2026

The best travel safety apps for business travel do three things well: they show your organization where its travelers are, they give each traveler a

A business man with a suitcase in the airport checking their phone
What Is Travel Risk Management?

Travel risk management is the structured process an organisation uses to protect its people when they travel for work. It covers four things: assessing

How to Travel Safely to COP31 in Antalya, Turkey

How to Travel Safely to COP31 in Antalya, Turkey The 31st UN Climate Change Conference (COP31) takes place in Antalya, Turkey from 9–20 November 2026,

An executive traveling with a carry on bag
Top Travel Risk Management Companies in 2026

The travel risk management (TRM) market in 2026 looks superficially similar to the market five years ago. The Travel Risk Management Companies most often shortlisted

Request ISO 31030 Consultation

Our risk consultants are ready to discuss your executive protection needs and develop a tailored solution for your organization.

What to Expect
1. Initial Response

Within 4 hours, a security consultant will contact you to understand your needs

2. Assessment

We'll conduct a thorough assessment of your Travel Risk Management

3. Custom Proposal

Receive a detailed support plan tailored to your specific needs

4. Seamless Implementation

4. Seamless Implementation

5. Ongoing Support

Get 24/7 access to our Global Assistance Center throughout your engagement

Contact Us

    * Required

    * By submitting this form, Sicuro Group may send you updates on products, services, and other content that may be of interest to you. Sicuro Group will also need to store and process your information, only for this purpose.

    Direct Contact
    24/7 Global Assistance Center

    +971 4 362 6378

    Delivering results with integrity
    Capability Backed by Compliance

    Our leadership team brings extensive field experience to every engagement. We emphasize ethical practices and adhere to global regulations and standards, positioning us as a trustworthy partner for organizations worldwide.

    ISO 9001

    Quality management — consistent delivery across every engagement, audited annually.

    ISO 27001

    Information security management for client data, intelligence and operational records

    ISO 22301

    Business continuity management — the framework behind our resilience consulting.

    ISO 31030

    Travel risk management — the global standard for organizations moving people across borders.

    GDPR compliant

    Full data-protection compliance for EU and UK clients — privacy by design across our platforms.

    US State Privacy Laws

    CCPA/CPRA aligned — privacy compliance for our US clients and their data.